Active · Baniloo Labs
Baniloo-Labs/loomedLooMed
A protocol for patient-controlled medical records. Portable, interoperable, and built without requiring hospitals to cooperate first.
This is an active project. The specification is evolving. These notes document the thinking as it develops.
Read the technical specification →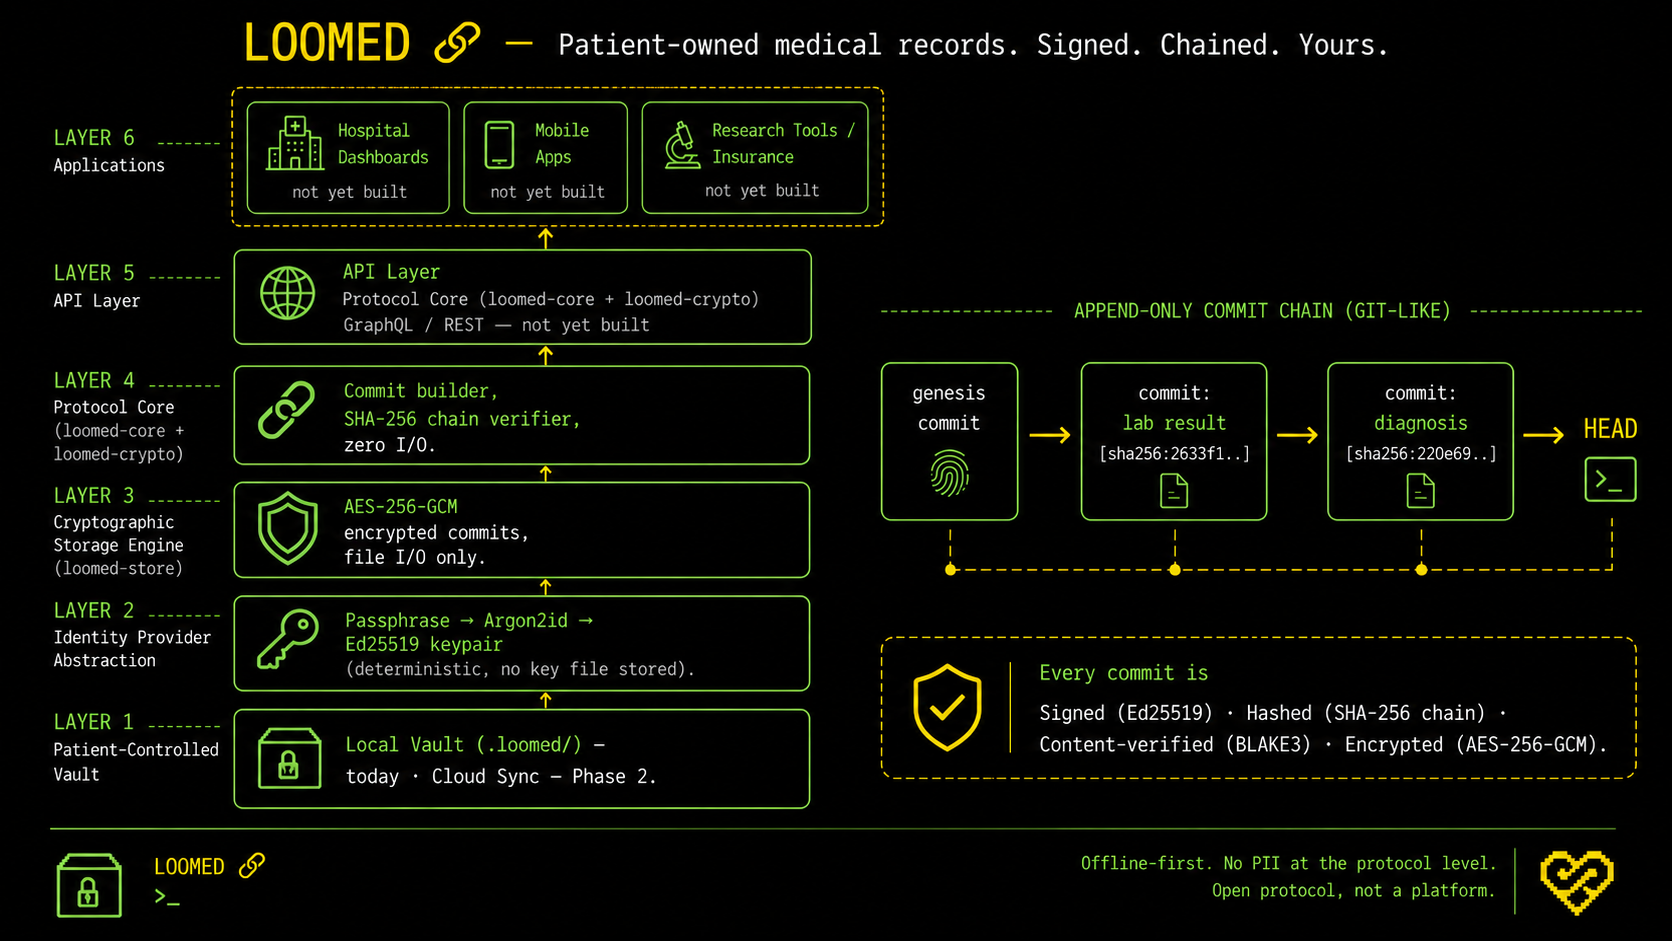
Thinking
Notes in reverse chronological order. Each entry is a piece of reasoning, worked through carefully.
Audit is a view, not a ledger
loomed audit and loomed revoke don't add a new commit log — they're both derived from the same chain scan that already answers whether a consent token has been used
The seam for an identity tier that doesn't exist yet
IdentityProvider gives LooMed one interface every future identity tier can implement with no call-site changes — and a BIP-39 recovery phrase whose entropy is the signing key, not a wrapper around it
Rotating the key that isn't the key you think it is
A vault passphrase derives two different keys — a signing key and an AES-256 encryption key. Key rotation only wanted to change one of them
The commit is the receipt
loomed commit --token makes a consent token actually enforceable — signature, expiry, access type, and scope checked in order, with no separate marker commit needed to make it single-use
A signature the institution can check without opening the vault
LooMed's consent tokens carry their own patient signature, independent of the chain — implementing spec §10.1's sign-then-embed flow for scoped, time-bound record access
The spec's own example IDs would have failed the checksum
Full Crockford Base32 + CRC-8 validation for LooMed participant IDs — and the illustrative examples in the spec and README that turned out to be fake
The chain survives the fork
Sync Rebase lands in Rust — deterministic fork resolution, signature preservation, and what pull and resolve mean as separate operations
The test suite that almost wasn't
34 integration tests, a Windows TTY problem, and what a protocol owes its future contributors
Phase 1 is complete
The local vault, the commit chain, and what was actually built
Why LooMed exists
Starting from the problem, not the solution